Fingerprint launches fraud rating system, reporting nearly 50% more fraud detected in customer tests – Unite.AI
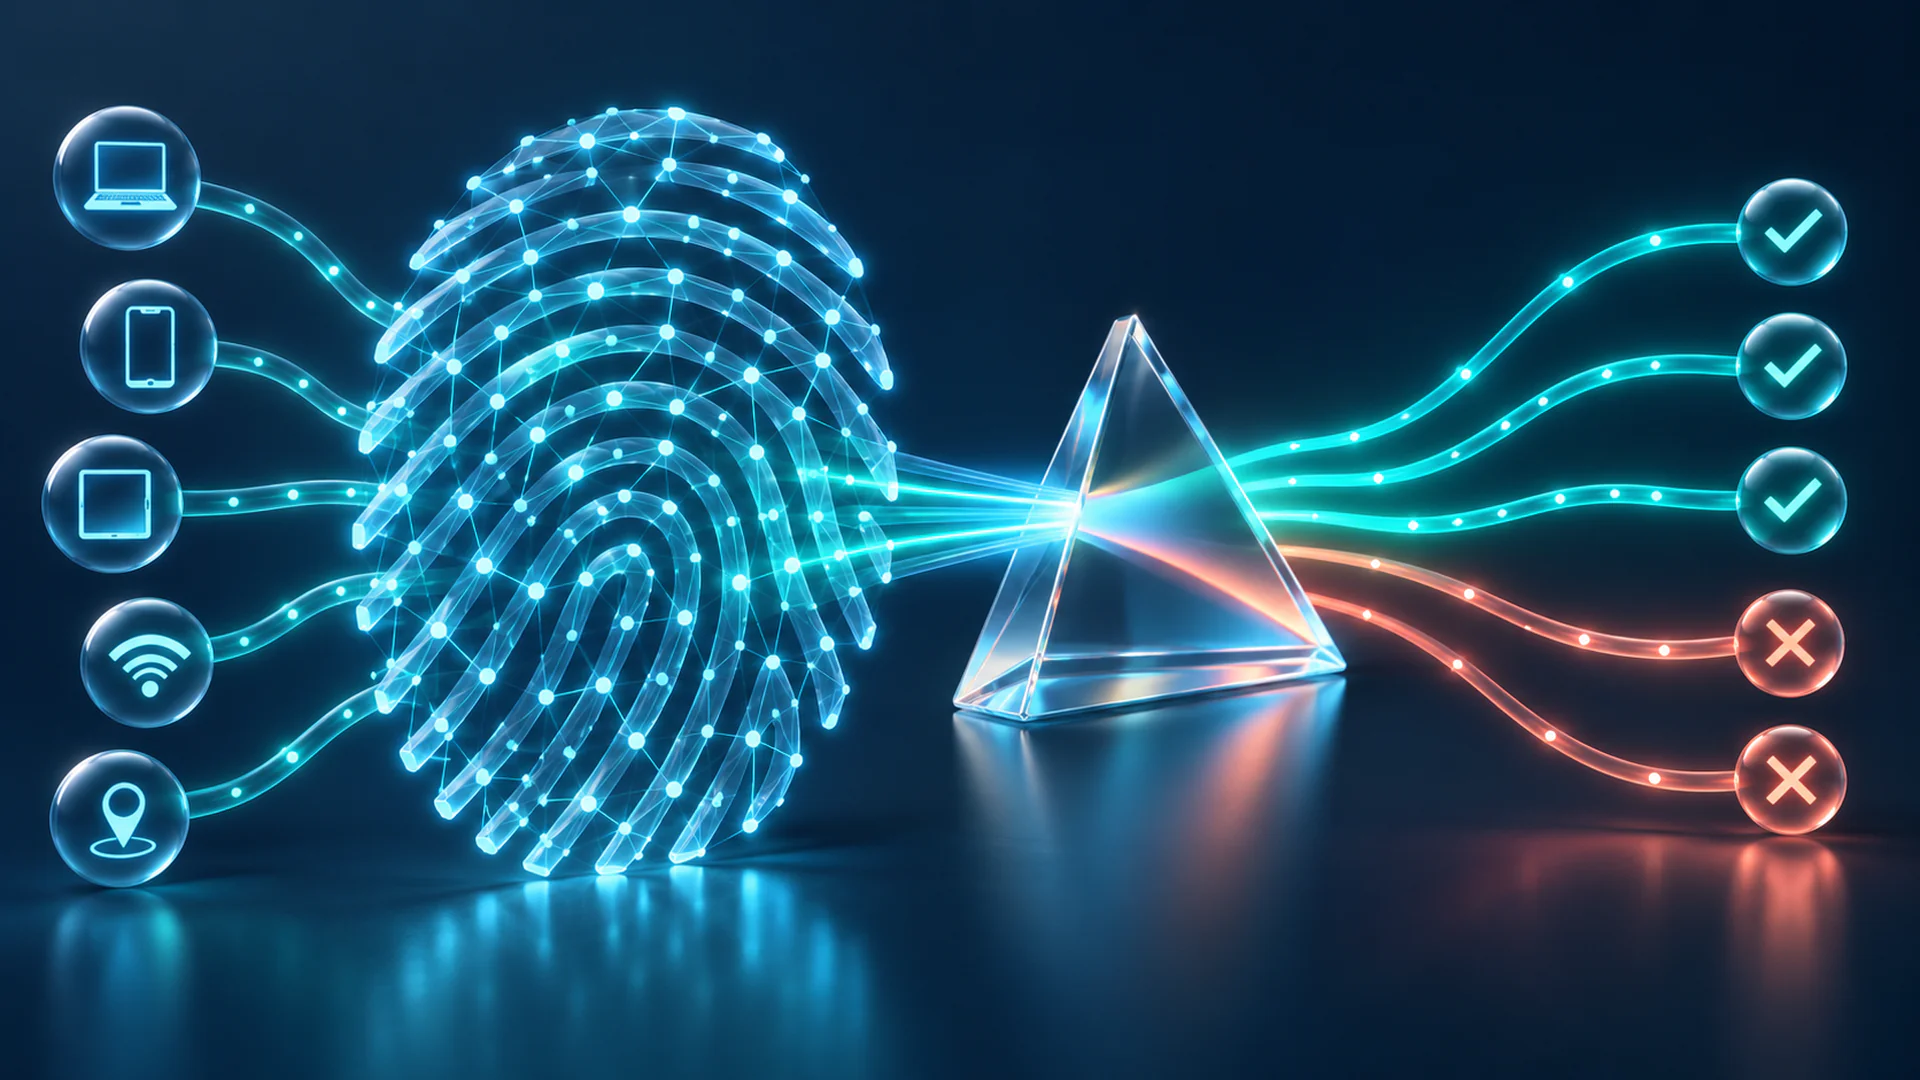
Fingerprint launched Fraud Score, a predictive fraud signal that combines device intelligence with machine learning models trained on each customer’s fraud outcomes. The company reports that in a comparative evaluation the product detected nearly 50% more fraud than a customer’s existing internal model, without increasing the number of legitimate users blocked.
The launch addresses a problem familiar to risk teams: Collecting signals is easier than turning them into a reliable decision. A device associated with multiple accounts may indicate promotion abuse, while an unknown device attempting to access a registered account may warrant a different investigation. Fraud Score is designed to learn these distinctions from an organization’s actual users, traffic, and confirmed results.
What the reported detection gain shows
The main result of Fingerprint concerns a comparison with a customer’s internal model. The company says Fraud Score detected nearly 50% more fraud at the same level of blocking as legitimate users. This second condition is consequential: a system can detect more suspicious activity simply by rejecting more traffic, but in doing so it can also drive away genuine customers.
The result comes from a direct comparison with a customer’s internal model. This demonstrates the importance of learning from a company’s fraud patterns while constantly blocking legitimate users.
The gain measures additional fraud detected. Its financial value depends on the transactions involved and how the company uses each forecast.
Separate models for different fraud problems
The central design choice of Fraud Score is to specialize predictions by type of fraud. Among the supported targets, Fingerprint lists payment fraud, account takeover, multi-accounting, fake account creation, promotion abuse, platform abuse, and content abuse.
These categories describe different business behaviors and costs. A payment fraud model might help a merchant price an order, while a promotion abuse model might look for repeated attempts to claim an offer across multiple accounts. An account takeover workflow has yet a different goal: detect unauthorized access without unnecessarily disrupting the legitimate account holder.
Customer results provide training feedback. Instead of asking each organization to create and maintain its own prediction layer, Fingerprint manages the training and maintenance of the models by combining device signals with company-provided labels. New findings fuel subsequent redevelopment as customer traffic and fraud patterns change.
This makes the quality of that feedback important. A model trained on confirmed results has more useful supervision than one trained on an undifferentiated list of suspicious events. If an organization’s labels are incomplete or inconsistent, the resulting predictions may reflect these limitations.
Device Intelligence provides context that goes beyond the account
Fingerprint’s device intelligence platform combines persistent identification with contextual signals about web and mobile activity. Its role is to help companies connect activity across sessions and inspect patterns that account details alone may not reveal.
The company’s Smart Signals catalog includes indicators of automation, browser tampering, virtual machines, proxies, VPNs, and unusually high device activity. These signals provide context for analysis; a privacy tool or an unknown environment does not in itself demonstrate fraudulent intent.
Fraud Score adds a customer-trained prediction layer to that evidence. The distinction is between recognizing an environment and evaluating how patterns in that environment relate to a particular company’s fraud outcomes. Teams can use the forecasts directly or feed them into an existing decision system alongside other information.
The approach goes beyond blocking an identifier already associated with abuse. A trained model can look for combinations of signals associated with previous cases, potentially helping a company recognize similar behavior before the next transaction is completed.
A feedback loop across dashboards, APIs and S3
According to Fingerprint’s launch materials, customers can provide fraud results via the dashboard, API, or S3. They can manage labels and analyze model performance, while predictions are provided via Fingerprint API responses.
This architecture fits into existing risk workflows. A decision engine can use prediction along with other controls to approve an interaction, request further verification, or route it for review.
Continuous redevelopment aims to make the service responsive to the evolution of abuse. The feedback loop still depends on what the organization learns after an event, including outcomes that may only become clear later. Monitoring model performance over time therefore remains part of the operation of the system.
Because Flink wanted more than just visitor ID blocking
The announcement includes an account from Flink, whose principal software engineer, David Fennessey, said that blocking visitor IDs alone is not sufficient against more sophisticated abuse. He described working with Fingerprint on a model based on Flink’s internal fraud analytics to help stop future abuse before an order is placed.
Flink’s experience illustrates the collaboration behind the service: the company contributes its internal fraud analysis, and Fingerprint uses that feedback to build and maintain a model tailored to its abuse patterns.
The Fraud Score shifts the emphasis from maintaining individual signals and rules to learning from a company’s results. Fingerprint manages training and retraining, while fraud teams maintain control over how predictions inform their decisions. The product is available via Fingerprint’s Fraud Score page.

Post Comment